Offensive security partnership

Offensive infostealer intelligence for red teams: Skip the break-in. Start from the foothold.

DeXpose gives red teams and penetration testers the credentials, session cookies and infected hosts that infostealers have already taken from the target, matched by domain in seconds. Weeks of reconnaissance become day-one access.

One intelligence layer behind every DeXpose product.

Public breaches, infostealer logs, combo lists and dark web sources, collected continuously and searchable by domain, email or keyword.

31BPublic Breachesrecords
58MCompromised Machinesdevices
2.2BInfostealer Recordsrecords
4.8BULPs & Combo Listsrecords
2BDarkweb Entriesentries
52KASNsnetworks
31BPublic Breachesrecords
58MCompromised Machinesdevices
2.2BInfostealer Recordsrecords
4.8BULPs & Combo Listsrecords
2BDarkweb Entriesentries
52KASNsnetworks
Infostealer intelligence

Every credential a stealer took from your target.

Infostealers like RedLine, Raccoon, Vidar, Lumma and StealC copy saved logins, cookies, sessions and autofill from infected machines. DeXpose ingests those logs from dark web markets, forums and Telegram, then lets you search them by domain, so you see exactly what an attacker already holds against your client.

  • Plaintext passwords, not just hashes
  • Live session cookies that can bypass MFA
  • The infected host, its OS and the malware family
  • Employee, customer and third-party logins
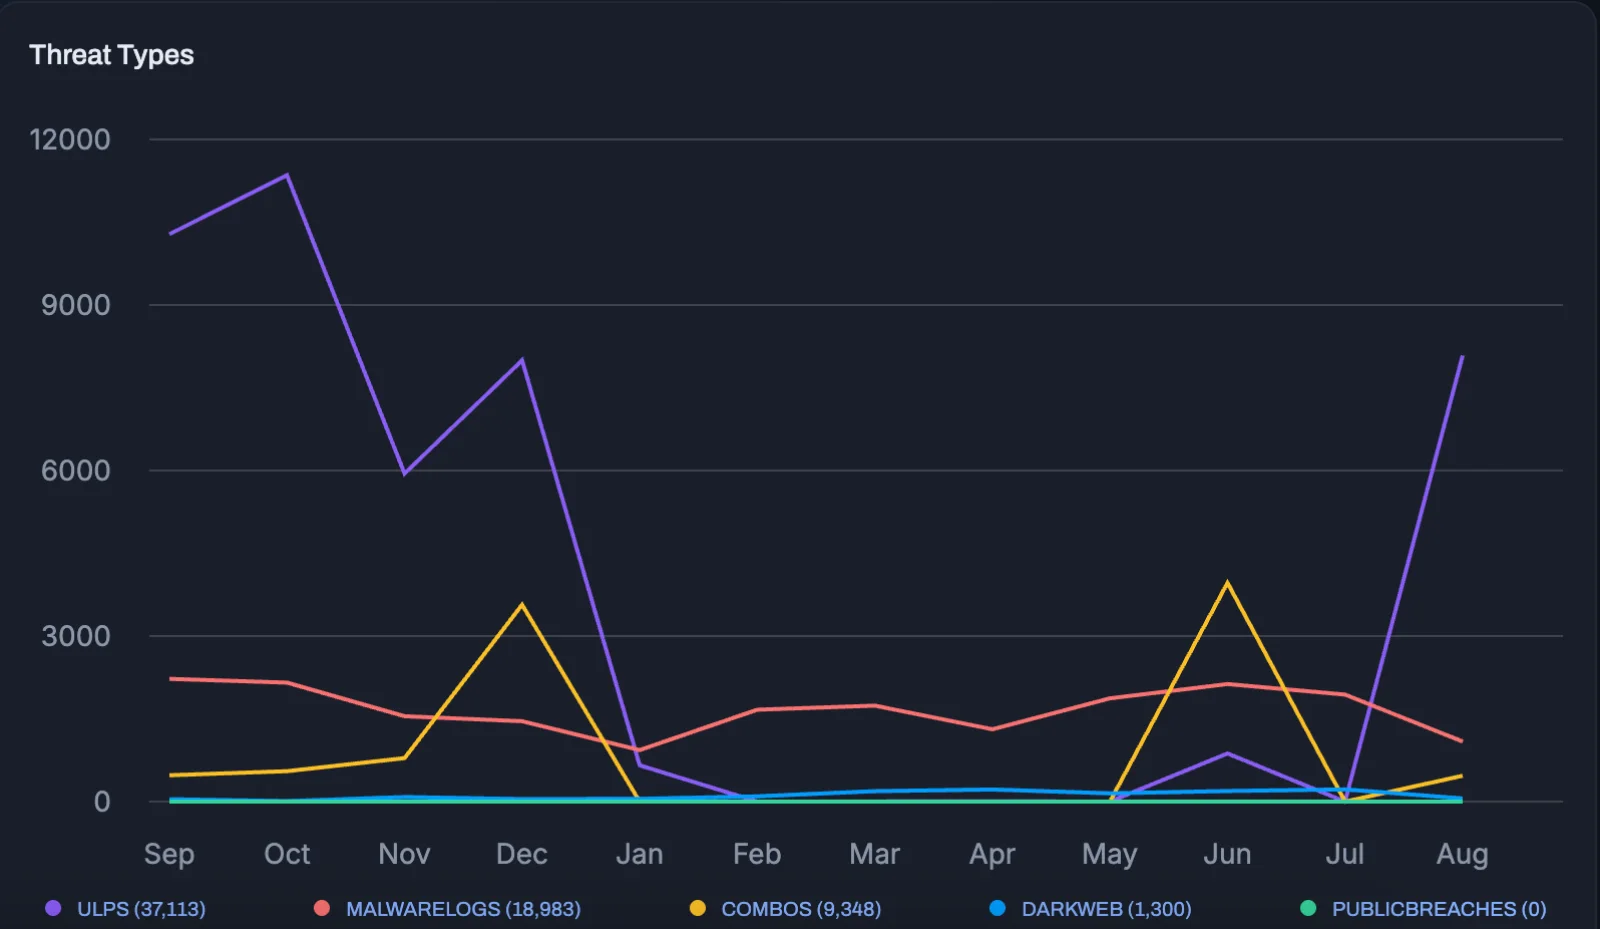
The threat types chart in the DeXpose dashboard: ULP dumps, malware logs, combo lists and dark web records by month
Threat types for one target over a year: ULP dumps, malware logs, combo lists and dark web records, in the DeXpose dashboard.
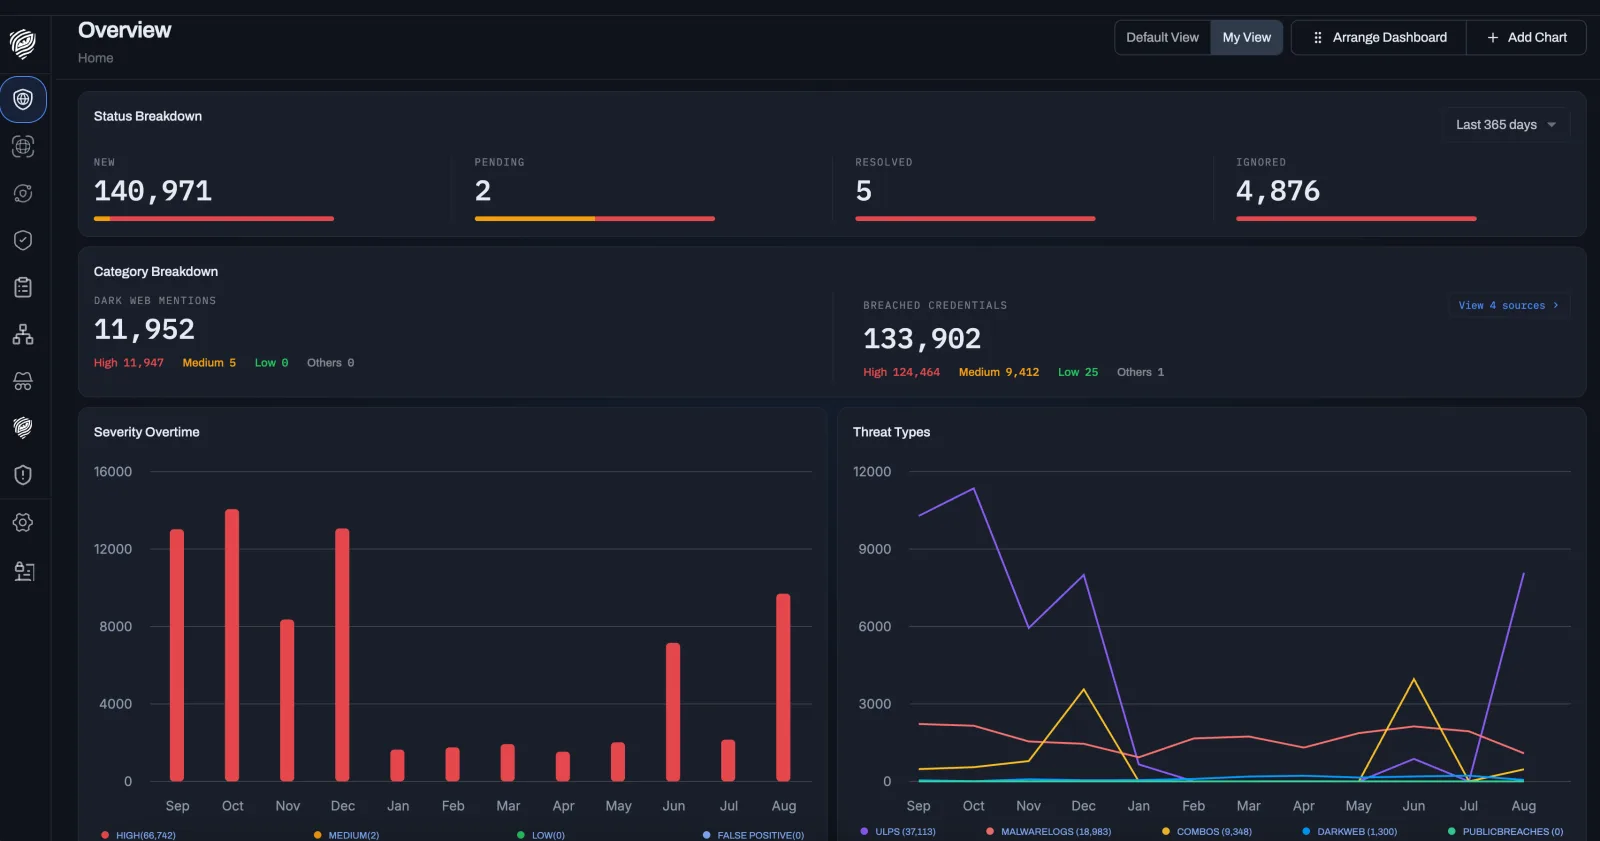
The DeXpose overview dashboard: status breakdown and category breakdown with dark web mentions and breached credentials rated by severity
Category breakdown for one target: dark web mentions and breached credentials, each rated high, medium or low.
Information gathering

Reconnaissance that starts inside the perimeter.

Before a single packet touches the target, DeXpose gives you the dark web view of your client: breached credentials, leaked secrets and API keys, exposed subdomains and infrastructure, and any ransomware or leak-site activity. Passive, external and invisible to the client. The same picture an attacker builds, delivered in minutes.

  • Breached credentials and combo lists
  • Leaked secrets, tokens and API keys
  • Subdomains, ASNs and exposed services
  • Dark web and ransomware leak-site mentions
In an engagement

From leaked login to proof of impact.

How red teams and penetration testers turn DeXpose intelligence into results: valid access on day one, findings the board understands, and less time spent on noise.

Talk to the partnerships team
  1. 1

    Reconnaissance

    Query the client domain and get the full exposure picture: compromised employees, infected hosts, leaked secrets and leak-site mentions. No scanning, no noise, nothing the client can detect.

    Before kickoff
  2. 2

    Credential access

    Test valid, already-leaked logins and reuse patterns instead of guessing. A live session cookie may walk you straight past MFA.

    Day one
  3. 3

    Targeted phishing and spraying

    Build convincing spear-phishing from real passwords and breach context, and prioritise the accounts and patterns most likely to work.

    Day one
  4. 4

    Proof of impact

    Show leadership the real dark web exposure behind their brand, with the source and date of every record, and make the case for the fixes that matter.

    Reporting

Red teams used to spend the first week of every engagement digging through dark web dumps by hand. Our partners open the engagement with valid credentials already in hand, and the client sees exactly why that matters.

DeXposePartnerships team, DeXpose
Built for your workflow

The same records, in the dashboard or in your tooling.

Search by hand during an engagement, or pull infostealer records, breached credentials and dark web signals straight into your scripts, C2 framework or reporting pipeline. Intelligence lives where your operators already work.

01Dashboard

Search a target, export the evidence

Query a domain, email or keyword and get compromised employees, plaintext passwords, live sessions and infected hosts in one view. Export what you need for the report.

  • Search by domain, email or keywordresults in seconds, with source and date
  • Per-client workspaceskeep every engagement separate
  • Report-ready exportsevidence with provenance for the client
02Data API

Grab-and-go REST, structured JSON

New stealer logs and breach data reach the API within minutes of collection. Query-count or per-client billing scales from one engagement to a whole practice.

  • Near real-time feedsminutes from collection to your pipeline
  • Pay as you goquery-count or per-client billing
  • Your data, isolatedeach partner runs in a dedicated instance
See the data partnership and API details
FAQ

Common questions.

Offensive infostealer intelligence, dark web monitoring and the API, in plain terms.

Running a practice, not a single test?

The partnerships team will walk through scope, billing and instance setup on a 30-minute call.

Talk to the partnerships team
What is offensive infostealer intelligence?

Infostealer malware harvests saved passwords, cookies, session tokens and autofill data from infected machines and ships them to the operator. DeXpose collects those stealer logs at scale from dark web markets, forums and Telegram channels, then makes the records searchable so red teamers can see exactly which of a client's credentials, sessions and hosts are already exposed.

How do red teams use DeXpose data in an engagement?

Query a client domain and get compromised employee logins, plaintext passwords, active session cookies, and the infected hosts behind them. That turns weeks of open-source reconnaissance into a starting foothold: valid credentials to test, real password patterns to spray, and session tokens that may still bypass MFA.

Is this available through an API?

Yes. The DeXpose API delivers infostealer records, breached credentials and dark web monitoring signals straight into your own tooling, C2 or reporting pipeline. Pay-as-you-go or per-client billing, near real-time feeds, and a grab-and-go REST interface. See the data partnership page for endpoints.

How fresh is the data?

New stealer logs and breach corpora are collected continuously and matched to your targets within minutes. Records carry the source, the collection date and whether the password is in the clear, so you can prioritise the credentials that still work.

Is this legal to use in penetration testing?

DeXpose provides intelligence about data that is already exposed. You use it only against clients who have authorised you in writing, within the scope of a signed engagement. It replaces the manual dark web digging red teams already do, with better coverage and an audit trail.

Give your red team an unfair advantage.

Partner with DeXpose for offensive infostealer intelligence and dark web monitoring, or run a free report on your next target's domain.