
What Is a Phishing Link? How to Spot, Check, and Recover From One
A phishing link is a URL designed to look legitimate, often mimicking a bank, retailer, or well-known app, but built to steal your credentials, install malware, or trick you into handing over personal information when you click it and interact with the page. It’s the delivery mechanism behind most phishing attempts: phishing remains one of the most common ways attackers gain initial access, and nearly every phishing campaign relies on a malicious link to do the damage.
Phishing links show up everywhere, in emails, text messages, DMs on Instagram or Snapchat, and even Discord invites, and they’re built to exploit trust and urgency rather than technical vulnerabilities, a core social engineering tactic. This guide explains what a phishing link is, how to recognize one, how to check a suspicious link before you click, and what to do if you’ve already clicked one.
What Is a Phishing Link?
A phishing link, also called a phishing URL, is a web address crafted to impersonate a trusted website or service so that you enter sensitive information, download malware, or authorize a fraudulent transaction. Unlike a broken or spammy link, a phishing link is deliberately engineered to look safe, often copying a real brand’s logo, domain structure, and page design almost exactly. You may also see it searched as a “phising link” or “fishing link”; the correct spelling is phishing, a play on fishing, because the link is the bait.
How Phishing Links Work
Phishing links work by exploiting the gap between how a link looks and where it actually goes. Attackers register domains that closely resemble a legitimate brand (swapping a letter, adding a hyphen, or using a different top-level domain), then wrap that address in familiar branding, a spoofed sender name, or a shortened URL to mask the destination. Once clicked, the link typically leads to a fake login page that harvests whatever you type, or it silently triggers a malware download in the background. These campaigns move fast and evolve constantly to dodge detection; of the roughly 100 million phishing emails Google blocks every day, 68% belong to campaigns that had never been seen before, which is why static blocklists alone rarely catch every threat.
Types of Phishing URLs
Not every phishing URL looks the same. The most common types are:
- Lookalike domains: a real brand name with one character swapped, added, or replaced (typosquatting).
- Subdomain tricks: the brand name placed in front of an unrelated domain, such as “yourbank.account-verify.com”, so the name appears first, but the real domain is different.
- Shortened links: URL shorteners hide the destination until after the click.
- QR-code links: a QR code printed or emailed so that scanning it opens a malicious URL, which hides the address from you entirely.
- Redirects and hijacked links: a link that starts on a trusted site or a compromised account and quietly forwards you to a phishing page.
Each type is built to hide the same thing: the real destination.
Phishing Link vs. Spam Link vs. Fake Website Link
A phishing link, a spam link, and a fake website link are related but not identical. A spam link is simply unsolicited; it might point to a real (if low-quality) product page or ad, with no intent to steal information. A scam link is the broadest label: any link meant to defraud you, including phishing, fake offers, and payment schemes. A fake website link is broader still, covering any site built to deceive, whether that’s a knockoff store or a scam giveaway page. A phishing link is the most targeted of the three: it’s specifically designed to impersonate a trusted entity and capture credentials or personal data, making it the version worth taking most seriously.
How to Spot a Phishing Link (Red Flags & Examples)
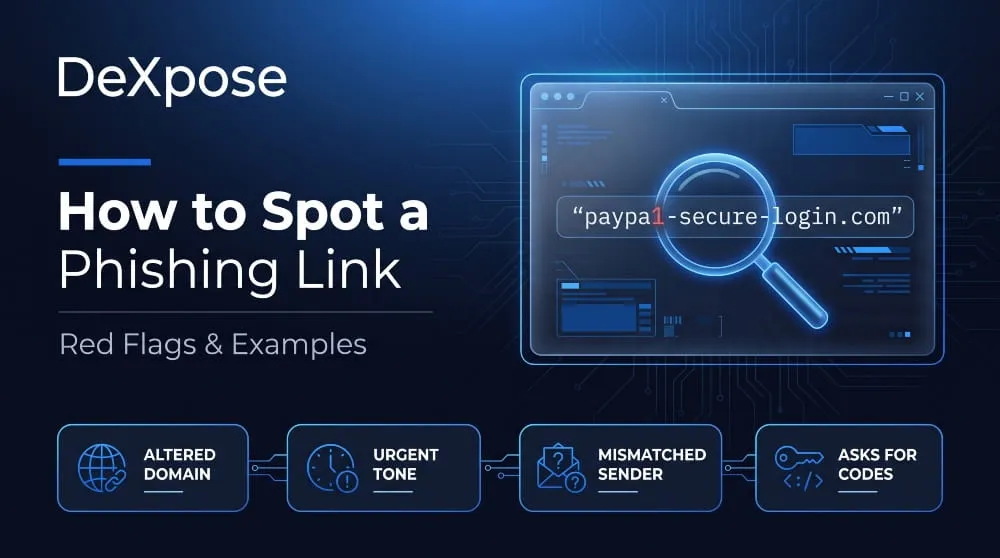
You can spot a phishing link by looking closely at the domain itself rather than the branding around it; the biggest tells are misspelled or altered domain names, urgent or threatening language, and a destination that doesn’t match the sender it claims to be. Most phishing links don’t need to fool an expert; they need to fool someone moving quickly, which makes phishing attacks easy to scale.
Common Phishing Link Examples
Phishing links tend to cluster around a handful of familiar disguises. A common example impersonates a shipping notification, “Your package couldn’t be delivered, click here to reschedule,” leading to a fake tracking page that asks for payment details. Another mimics a security alert from a major platform, warning that an account will be suspended unless the recipient “verifies” their login within 24 hours. A third imitates an invoice or payment request, often targeting employees on behalf of a vendor or executive. These templates work precisely because they borrow the visual identity of brands people already trust. In Q3 2026, Check Point Research found that Microsoft accounted for 33% of all brand impersonation attempts, roughly four times the share of any other brand, and attackers are now imitating AI and developer platforms as well. The logo at the top of a page is rarely a reliable signal of safety.
What Does a Phishing Link Look Like?
On the surface, a phishing link can look almost identical to a real one. The difference is in the domain, the registered name that sits just before the first single slash in the address. These examples are illustrative, not real sites:
Telltale Signs a Link Isn’t Legit
A few consistent signs separate a phishing link from a legitimate one, even when the page design looks convincing. The visible link text and the actual destination URL don’t match when you hover over it. The domain includes extra words, hyphens, or a different extension than the real site (a bank’s domain ending in “.security-check.com” rather than its actual domain, for instance). The page asks for information a legitimate service would never request over email or text, such as a full password or one-time verification code. And the message creates pressure to act immediately: a locked account, a missed delivery, a limited-time refund, because urgency is what stops people from checking the link first.
How to Check if a Link Is Phishing
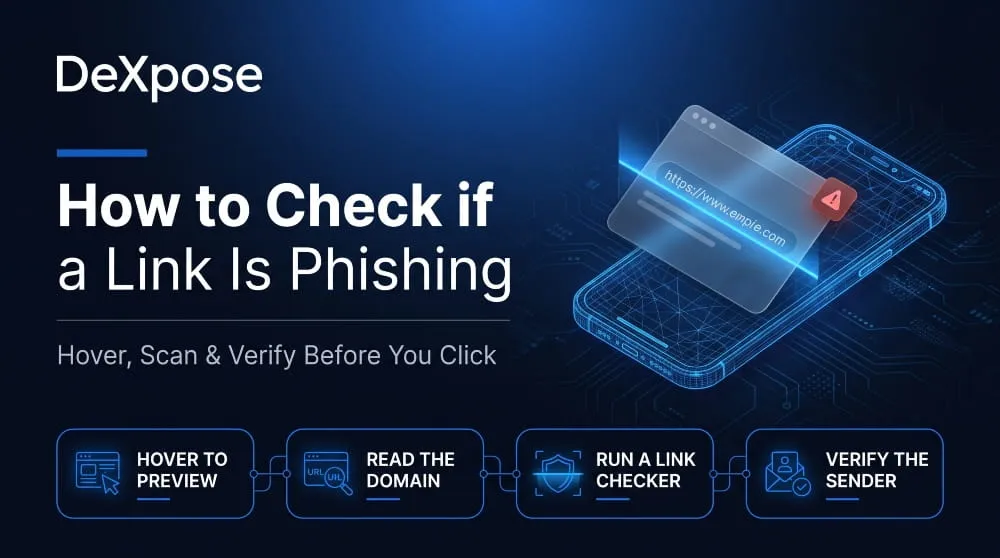
The fastest way to check if a link is phishing is to inspect the actual destination URL before clicking, either by hovering over it or running it through a dedicated link checker, rather than trusting how the link looks or where it claims to be from.
Using a Phishing Link Checker Tool
A phishing link checker (sometimes called a phishing link detector or URL scanner) scans a URL against databases of known malicious domains, flags suspicious patterns like lookalike spelling or newly registered domains, and often previews the page’s content without exposing your device to it. Free options include Google’s Safe Browsing site status page, VirusTotal, and urlscan.io. This is the most reliable option when a link arrives from an unfamiliar sender or when the destination isn’t obvious from the text alone. Paste the full URL into the checker rather than a shortened version, since shortened links are frequently used specifically to hide the real destination, and never paste links that contain personal tokens, such as password-reset links, into a third-party tool. These tools matter because habits alone aren’t foolproof: even security-aware employees still click convincing phishing attempts, though awareness training has been shown to cut phishing simulation click-through rates by 32% compared with untrained staff; a checker tool helps close the gap that training doesn’t.
Manual Verification Steps (Hover, Preview, Domain Check)
Manual verification starts with hovering over the link on desktop (or long-pressing on mobile) to preview the actual URL in a tooltip or status bar, without clicking through. From there, check the domain itself: read it right to left, since attackers often bury the real brand name inside a longer, unrelated domain (like “microsoft-login.secure-verify.net” rather than an actual Microsoft address). Look for HTTPS and a valid certificate, though note this only confirms an encrypted connection, not that the site is legitimate, since phishing pages can carry valid certificates too. Finally, cross-check the sender: if an email claims to be from your bank but the link points to a domain unrelated to that bank, that mismatch alone is enough to treat the link as unsafe.
I Clicked on a Phishing Link, What Do I Do Now?
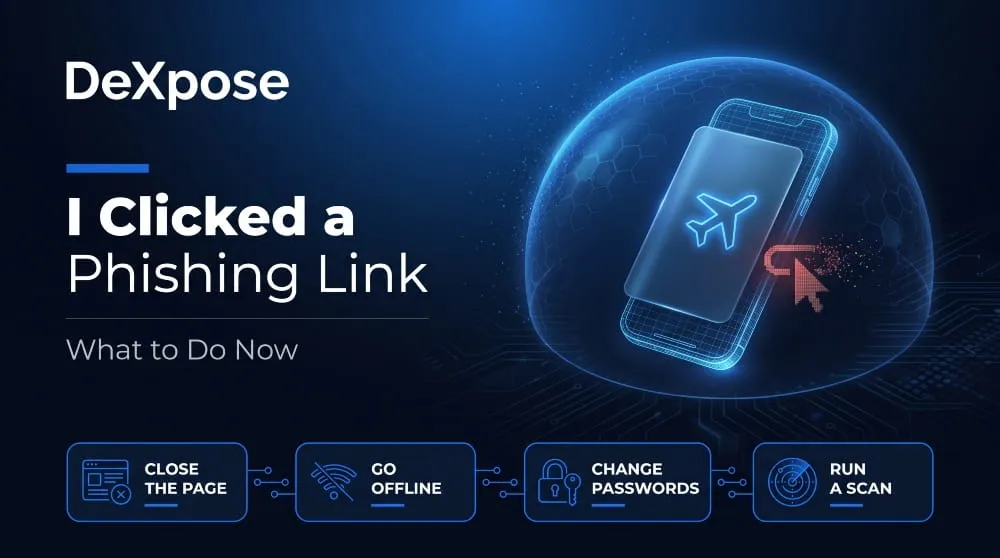
If you’ve clicked on a phishing link, the priority is to stop before entering any information, disconnect from the internet, and then work through a short checklist based on what you did next, whether you entered data, closed the page immediately, or aren’t sure. Clicking alone rarely causes damage; what happens after the click is what determines the outcome.
Immediate Steps (Disconnect, Don’t Enter Credentials)
The moment you realize a link is phishing, close the page without typing anything, and disconnect the device from Wi-Fi or cellular data, especially if you’re not sure what the page loaded. This limits any malware on the page from communicating with an attacker’s server or downloading further payloads. Don’t enter a username, password, verification code, or payment details even if the page looks legitimate; a phishing page’s entire purpose is to capture whatever you type, and once submitted, that data is typically out of your control within seconds.
What to Do If You Entered Personal Information
If you entered a password, verification code, or financial details, change that password immediately from a separate, trusted device, not the one you clicked the link on, and do the same for any other account reusing that password. Enable two-factor authentication if it isn’t already active, contact your bank or card issuer if payment information was involved, and monitor the affected account closely for unrecognized activity over the following days. If a work account was involved, report it to your IT or security team right away; delayed reporting is often what turns a contained incident into a wider breach. Also report the link itself to the impersonated company and your email or messaging provider; our guide on how to report phishing explains where to send it.
What to Do If You Clicked But Closed the Page Immediately
Closing the page immediately without entering information is low risk, but it’s not automatically safe. Some phishing pages attempt a drive-by malware download the instant they load, before you’ve typed anything. As a precaution, run a security scan on the device, watch account activity for the next week or two, and treat any follow-up messages from the same sender with extra suspicion; a second attempt often follows the first.
iPhone- and Android-Specific Steps
On iPhone, clicking a phishing link rarely installs malware directly, since iOS sandboxes apps and browser sessions tightly. However, you should still update to the latest iOS version, check Settings for any unfamiliar configuration profiles, and change any passwords entered on the page. On Android, the risk is higher if the link led to a prompt to install an app or profile outside the Play Store; decline any such install, and if one already went through, uninstall it immediately and run a mobile security scan (see our guide to checking a phone for malware), since Android’s more open app-installation model makes it a more common target for link-based malware than iOS.
Phishing Links on Specific Platforms
Phishing links adapt their disguise to whatever platform they’re sent through, but the underlying goal stays the same: impersonate something the recipient trusts enough to click without thinking. Tactics differ slightly by platform because the trust signals people rely on (a verified badge, a friend’s account, a familiar game invite) also differ.
Social Media (Instagram, Facebook, Snapchat, TikTok, X/Twitter)
On social platforms, phishing links most often arrive through direct messages from compromised or cloned accounts, fake “someone shared a post about you” notifications, or comments promising followers, giveaways, or verification badges. Instagram and Facebook phishing links frequently mimic a copyright-strike or account-suspension warning to pressure a quick login; Snapchat and TikTok versions lean more on prize giveaways or “who unfollowed you” curiosity hooks. Because these messages often come from a real friend’s hacked account rather than an obvious stranger, they tend to bypass the skepticism people apply to email, so treat any unexpected link in a friend’s DM as unverified and confirm it through another channel.
Gaming & Chat Apps (Roblox, Discord, Steam, Fortnite)
Gaming and chat platforms see phishing links dressed up as free in-game currency, item trades, or “double your skins” offers, usually sent through direct messages or posted in public servers. Roblox phishing links commonly promise free Robux in exchange for logging into a fake site; Discord versions often mimic a “free Nitro” gift link sent from a compromised friend’s account; Steam and Fortnite phishing attempts frequently pose as trade offers or account-recovery requests. These links target account credentials and linked payment methods specifically, since gaming accounts often carry real monetary value through skins, currency, or saved purchase details.
Email & Messaging (Gmail, WhatsApp, Telegram)
Email and messaging apps remain the most common delivery channel for phishing links, typically disguised as security alerts, delivery notifications, or messages from a known contact. Gmail phishing links often imitate a “suspicious sign-in” warning designed to capture the actual Google password while “verifying” it. WhatsApp and Telegram phishing links tend to spread through forwarded messages claiming a prize, a job offer, or an urgent request from a contact whose account has already been compromised, since a message arriving from someone already in your contacts list carries far more built-in trust than a cold email ever would. Plain SMS has its own tricks; see our guides to phishing text messages and smishing for text-based examples.
How to Protect Yourself From Phishing Links
Protecting yourself from phishing links comes down to two things: building habits that make you naturally suspicious of unexpected links, and backing those habits up with tools that catch what attention alone will miss. Neither one is sufficient on its own; habits slip under time pressure, and tools can’t stop you from typing a password into a page you never checked.
Safe Link-Checking Habits
The strongest habit is treating every unexpected link as unverified until proven otherwise, regardless of who it appears to come from. That means previewing the destination as described above, typing a company’s URL directly into the browser instead of clicking a link in an email or text, and pausing on any message that creates urgency around an account, payment, or deadline. Enabling multi-factor authentication is one of the highest-leverage habits available, since it limits the damage even when a phishing link succeeds. Microsoft research found that MFA reduces the risk of account compromise by more than 99%, which means a stolen password alone usually isn’t enough to get an attacker in. MFA isn’t bulletproof, though: attackers can relay one-time codes in real time through a fake login page, so passkeys or hardware security keys, which won’t work on a lookalike domain, are the stronger option where available.
Tools and Extensions Worth Using
Beyond manual habits and link checkers, a handful of tools add a consistent safety net: browser extensions that flag known malicious domains before a page loads, email and messaging filters that catch phishing attempts before they reach an inbox (see our guide to phishing protection), and password managers that refuse to autofill credentials on a lookalike domain, a quiet but effective signal that something’s off. For anyone managing multiple accounts or a business’s exposure, dark web monitoring adds another layer by alerting you if compromised credentials tied to a phishing link ever surface in a breach dump, closing the loop between a click that already happened and the fallout it could still cause.
Check your exposure with DeXpose. If a phishing link may have captured your login, run a free dark web report for your domain or an email data breach scan to see whether credentials have already surfaced. Organizations that need to catch lookalike domains and phishing pages impersonating their brand can learn more about DeXpose Brand Protection.
Frequently Asked Questions (FAQs)
What should I do if I clicked a phishing link but didn’t enter any information?
Close the page, briefly disconnect from Wi-Fi, and run a quick malware scan. The risk is low, but not zero, since some pages try to download silently on load.
How do I know if a link is fake before clicking it?
Hover over it to preview the actual destination, and check whether the domain matches the sender it claims to be from.
Can clicking a link alone get my device hacked?
It’s possible but uncommon; most damage comes from what happens after the click, entering credentials or approving a malicious download, rather than the click itself.
What does a phishing link do?
A phishing link sends you to a fake page that captures whatever you type, or triggers a malware download. The link is only the delivery mechanism; the damage comes from the credentials, codes, or payment details you hand over.
Can I check a link without clicking it?
Yes. Hover over it (or long-press on mobile) to preview the destination, then paste the full URL into a phishing link checker such as Google’s Safe Browsing site status page, VirusTotal, or urlscan.io.
How do I report a phishing link?
Report it to the impersonated brand, your email or messaging provider, and your IT team if it reached a work account. Our guide on reporting phishing includes the steps.
How to Check for Malware on Mac, Windows and PC (Scan, Detect and Remove It)
How to Check Your Computer for Malware To check for malware, run a full scan with your operating system’s built-in security tool, then review the apps,…
Read more
Malware on Phone | How to Check, Scan and Remove It on iPhone and Android (2026 Guide)
You can check a phone for malware by reviewing installed apps, permissions, battery and data usage, and unknown profiles, then running Google Play Protect on Android.…
Read more
Malware Protection | The Complete 2026 Guide to Protecting Your Devices, Data and Network
Malware protection combines software, settings, and habits to detect, block, and remove malicious programs before they steal data, lock files, or take control of a device.…
Read more